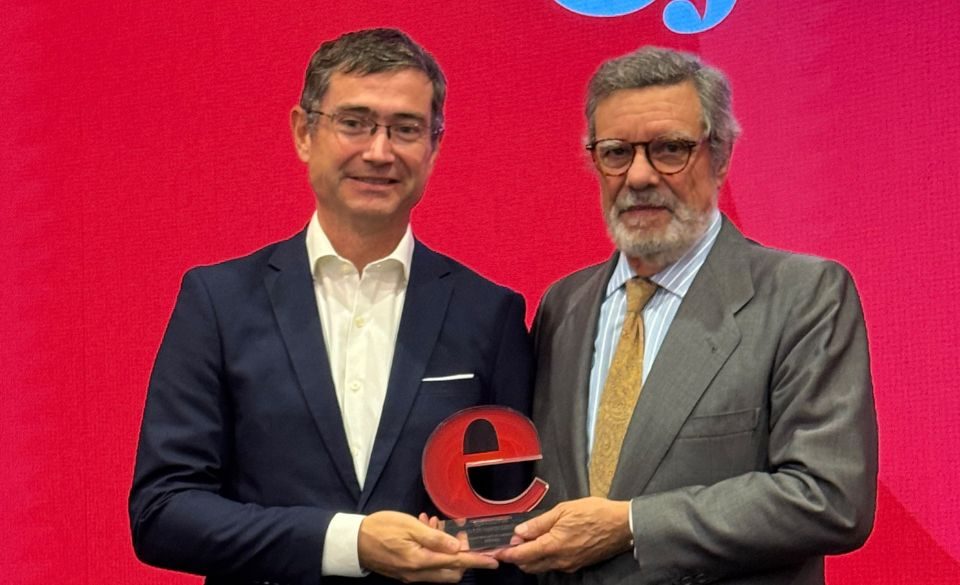
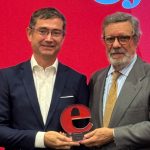
Cosmikal receives the 2026 Ejecutivos Award for Breakthrough Cybersecurity Vendor
9 de October de 2026
On the night of October 11–12, 2026, hundreds of French supermarkets saw their cold-storage rooms heat up without anyone in the stores ordering it. According to Les Mousquetaires, owner of Intermarché, the cold-storage rooms at around 150 of its stores remained at 50°C for six hours (Reuters).
This was not an attack on data, but on the physical world, and, according to published reports, it may have been carried out through something as commonplace as remote access to maintenance equipment.
What happened in the supermarkets?
- France. Economy Minister Roland Lescure put the number of affected supermarkets at around 700. Carrefour confirmed 80 stores and Monoprix 5%; estimates for affected Intermarché and Netto stores range from 150 to 300 depending on the source (Reuters, TIME, AP). The Paris Public Prosecutor’s Office is investigating, including possible fires. No one has claimed responsibility for the attack (FreshPlaza) and, according to AP, there does not appear to have been a ransom demand.
- Official response. The prime minister tasked ANSSI, the French cybersecurity agency, with the investigation, and France is coordinating its response with other European countries. Its response team, CERT-FR, issued alert CERTFR-2026-ALE-012 on October 12 regarding numerous compromises of remote refrigeration controllers and expanded it to other equipment on October 13.
- Netherlands, a separate case. Ahold Delhaize shut down systems as a precaution following a cybersecurity incident and said there was no reason to link it to France. No connection has been confirmed (FreshPlaza).
How did they do it?
The entry vector has not been officially confirmed. This is what the sources indicate:
- An internet-accessible panel. The panels that manage all the refrigerators and freezers in a store can often be reached over the internet so maintenance companies can adjust them remotely. CERT-FR notes that exposing a management interface on the internet runs counter to best practices, and France accounts for almost 60% of that manufacturer’s controllers exposed worldwide, according to U.K. Cyber Defence (TIME).
- Old or unpatched equipment. The manufacturer said the affected units were running outdated firmware and that most were older products without software or security updates. In August, Claroty had disclosed vulnerabilities in one of its models that the manufacturer had already fixed (Reuters). Investigators have not yet made public how the attackers gained access (TIME).
- A legitimate function used maliciously. According to BFM-TV, the attackers forced a continuous defrost cycle with a 50°C setpoint and, according to Le Monde, extended the cycle from one to eight hours in some freezers and cold-storage rooms to delay the alarms. Christopher Whyte of Virginia Commonwealth University told AP that such an attack is not particularly difficult and that the controls were most likely open to the supermarket network.
The attackers did not break the refrigeration system: they used a normal system function—defrosting—through its management console.
What is the cost of an attack like this?
Financial. Thierry Cotillard, president of Intermarché, estimated losses in the tens of millions of euros across France in a single day. Two supermarkets in Alsace reported losses of €270,000 (BFM-TV, via TIME). Intermarché warned AFP that some insurance policies do not necessarily cover this type of incident, and CERT-FR recommends checking insurance terms before cutting the data connection with the refrigeration company.
Reputational. Lescure said there was no risk to the food supply, but that the attack strikes at the heart of the country’s food security and serves as a warning to everyone. Dominique Schelcher of Coopérative U called it unprecedented and extremely serious. The groups discarded all affected products to eliminate any health risk, and the French retail federation called for full transparency from the software provider (Reuters).
Operational and energy-related. Frozen-food aisles were closed, and the Public Prosecutor’s Office is investigating fires in some cold-storage rooms (AP). None of the sources consulted has published figures on the energy cost of restarting the machines or the additional cost of replacing food. In the Netherlands—a separate case—the precautionary shutdown of Ahold Delhaize systems halted Albert Heijn distribution centres and left stores short of fruit and vegetables; customers who had already paid will be compensated (FreshPlaza).
Why it matters beyond France
Ken Munro of Pen Test Partners described it to Reuters as basic cyber hygiene (Euronews). CERT-FR warns that attack campaigns against this equipment are probably still under way and that leaving equipment exposed without security patches makes compromise highly likely. Connected physical equipment with third-party remote access is a critical asset and must be protected accordingly.
How Endurance could have helped
Cosmikal is a Spanish cybersecurity manufacturer, and Endurance—our Remote Shielded Workspace (RSW) solution—integrates PAM, VDI, IAM and DLP capabilities to protect access to critical assets. If the refrigeration management systems had been operated through Endurance:
- The Asset is not exposed on the internet. Access takes place within the protected RSW environment: there is no exposed console to discover.
- RSW isolates the Asset, not the endpoint. There is an air gap between the technician’s device and the Asset. Even if the maintenance provider’s device were compromised, it would not affect the connection or the Asset.
- External maintenance providers follow the same rules as everyone else. Endurance applies company policies to every requester: verified identity, least privilege, access windows and traceability. An out-of-hours defrost cycle can be restricted or approved, but it will always be logged.
- Browser-based access is governed in the same way as any other protocol.
This drastically reduces the likelihood that the most frequently cited route—an exposed console with third-party remote access—can be exploited, in line with CERT-FR’s recommendation to restore access only through a protected network or a secure VPN.
What no platform can solve on its own. The entry vector has not been officially confirmed. Unsupported firmware remains a risk; an attacker already inside the local network requires dedicated segmentation and detection; and maintaining an inventory of connected equipment remains the first step.
Five actions to prevent these attacks
- Identify what responds from the internet on your public IP addresses and cross-check the results against the maintenance provider’s inventory.
- Remove direct exposure of every management console.
- Define in maintenance contracts how third parties gain access, which identity they use, during which hours and with what audit trail.
- Separate the physical-equipment network from the office network.
- Add temperature sensors independent of the central controller: they provide alerts even if it fails or is manipulated.
Sources (accessed October 15, 2026):
- CERT-FR (ANSSI): alert CERTFR-2026-ALE-012 (Oct. 12 and 13)
- Reuters: Hackers raise fridge temperatures at hundreds of French supermarkets to spoil food (Oct. 13)
- Associated Press: Cyberattacks hit European supermarket chains and disrupt refrigeration systems (Oct. 13)
- TIME: Cyberattack on Supermarket Fridges in France Highlights Food Systems’ Vulnerability (Oct. 13)
- Euronews: Thousands of refrigerators in French supermarkets remain exposed (Oct. 14)
- FreshPlaza: French, Dutch, and Belgian retailers deal with cyber incidents and attacks (Oct. 13)
- MacGeneration, based on reporting by AFP: Refrigerators set to 50°C (Oct. 12)