
Cybersecurity in the energy sector: the risk of a remote connection compromising continuity of supply
22 de October de 2026
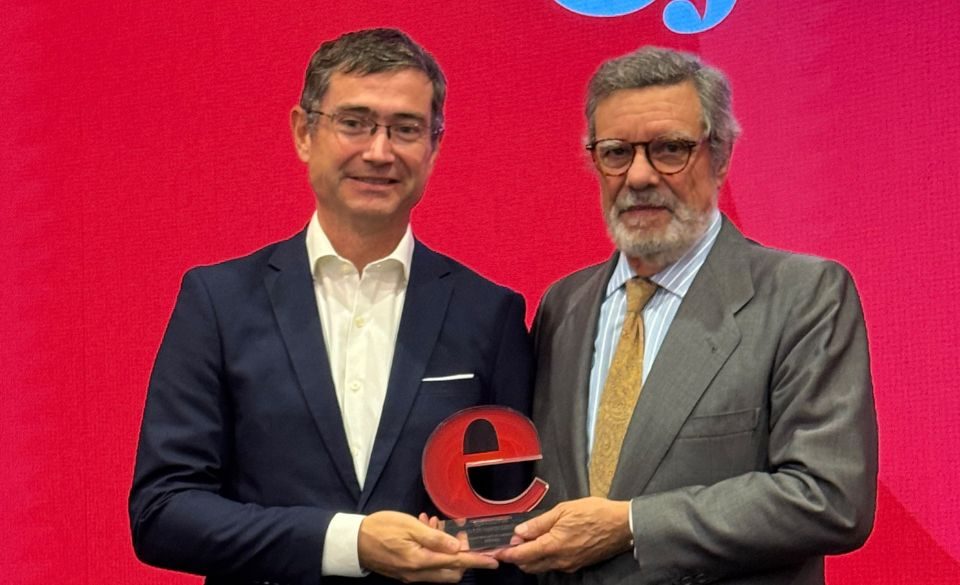
If scheduling obligations or operational commitments prevented you from traveling to León between October 21 and 23 for the 20th International Information Security Meeting (#20ENISE), do not worry. At Cosmikal, we have compiled this post covering what happened at the León Conference Center: strategic debates, regulations that are changing the rules of the game, and the roadmap that will shape cybersecurity in Spain and Europe over the coming year.
As cybersecurity solution manufacturers, we were not only there to engage with more than 4,000 industry professionals, but also to actively analyze where the market is heading. The conclusion is clear: the model of dependence on foreign technology has run its course; the era of resilience and digital sovereignty has begun.
1. #20ENISE: technological sovereignty is no longer just a theory
While previous editions focused mainly on awareness and the adoption of defensive tools, this 20th anniversary has established one fundamental concept: strategic technological sovereignty.
Against a backdrop of global geopolitical instability and uncertainty in the international supply chain, the industry has reached a unanimous consensus. Being protected is not enough; it is essential to know who builds the security software, which laws govern it, and where the data and detection intelligence reside.
Cosmikal’s Perspective as a Manufacturer
In the panel discussions and corridors of León, we advocated a principle that directly aligns with the European regulator’s vision:
- True operational autonomy: The security of our public administrations and critical infrastructure cannot depend on international “black box” solutions exposed to regulatory shifts or corporate decisions made outside the EU.
- Native code and design: Developing proprietary technology in Europe makes it possible to audit, verify, and adapt tools to European legal frameworks (such as NIS2 and the CRA) from the very first line of code.
2. The four key themes that dominated León 2026
For those seeking a structured overview of the event, its content revolved around four major themes:
A. The Cyber Resilience Act (CRA) comes into play—and the end of “black boxes”
For the first time, the Cyber Resilience Act imposes strict legal responsibilities on software developers and hardware manufacturers. The following topics were examined in detail:
- Transparent vulnerability management and reporting: The key role of National Certification Authorities (CNAs) and coordinated disclosure standards.
- Sustainability and lifecycle: Manufacturers will be required to guarantee support, patches, and code transparency throughout the product lifecycle.
- Software supply chain transparency (SBOM): Organizations now demand precise visibility into the components included in their security tools.
B. Operational rollout of the NIS2 Directive and protection of critical sectors
With transposition and compliance deadlines underway, the ecosystem’s concern shifted from theory to day-to-day practice.
- Real-world adaptation cases were examined in sectors such as energy, transport, banking, and healthcare.
- The central message for CISOs was unequivocal: governance and operational resilience take precedence over simply accumulating disconnected tools.
C. Artificial Intelligence: from automated detection to explainability
AI was examined from two opposing perspectives:
- Offensive AI vs. Defensive AI: The increased speed of AI-driven cyberattacks requires autonomous orchestration and response platforms capable of reacting in milliseconds.
- Data sovereignty and ethics in AI: The most highly praised talks stressed the importance of not training security AI models outside European regulatory borders, thereby protecting the confidentiality of local threat intelligence.
D. Digital identity, trust, and post-quantum cryptography
Identity management in Zero Trust and hybrid environments, together with planning the transition to quantum-resistant algorithms, took center stage in the most technical workshops on the third day.
3. Essential talks and panel discussions
If you plan to spend time reviewing the official #20ENISE recordings or proceedings, we recommend focusing on the following sessions:
| Session / Track | Main Topic | Key Takeaway |
| Institutional opening and INCIBE | National Cybersecurity Strategy and investment in the domestic ecosystem. | Strong support for the growth of local manufacturers and startups to strengthen the industry. |
| Panel of CISOs from essential infrastructure organizations | Practical challenges of implementing NIS2 in IT/OT environments. | Integration with local manufacturers accelerates incident resolution without bureaucratic friction. |
| Cyber Resilience Act (CRA) Panel | New quality and security requirements for software manufacturers. | It signals the end of software without guarantees, requiring traceability and transparency in security engineering. |
| Threat intelligence keynote | Evolution of the global cyber threat landscape in 2026. | Public-private collaboration and the sovereign exchange of IOCs (indicators of compromise) are essential. |
4. Cosmikal at #20ENISE: strengthening our proprietary manufacturing model
For the Cosmikal team, #20ENISE was a key event where we were able to validate our technological proposition against real market needs:
- Meetings with clients and partners: We confirmed that companies and public institutions are redirecting their investments toward manufacturers capable of providing a close working relationship, specialized support, and built-in regulatory compliance.
- Platform demonstration: We showed how our solutions deliver security and control without compromising data sovereignty or creating dependencies on third parties.
- Commitment to the ecosystem: We formed strategic alliances with other stakeholders across the Spanish and European technology landscape to continue building a robust cybersecurity ecosystem.

Conclusion: where we should look after #20ENISE
ENISE’s 20th anniversary not only celebrated two decades of progress; it also marked the beginning of a period in which technological sovereignty becomes a competitive advantage and a guarantee of corporate survival.
If you would like to explore any of the topics discussed in León in greater depth, or discover how our proprietary cybersecurity solutions can help your organization meet the new European resilience and sovereignty requirements:
Contact the Cosmikal technical team